
Cybersecurity
Security reviews, access controls, SSL, form protection, dependency checks, hardening, and secure deployment practices.
Let’s plan your projectA clear scope. A useful outcome.
Infrastructure should support reliable delivery instead of becoming a source of uncertainty. We review the workload, recovery needs, and team responsibilities, then build a practical operating model for the environment.
For cybersecurity, we define the first useful deliverable, the systems it depends on, and how your team will review the result.
Prioritize the risks to your systems
Understand the systems, identities, and information that need protection. Prioritize findings by their relevance to the application and business workflow.
- Application and dependency review
- Account and access assessment
- Sensitive data flow mapping
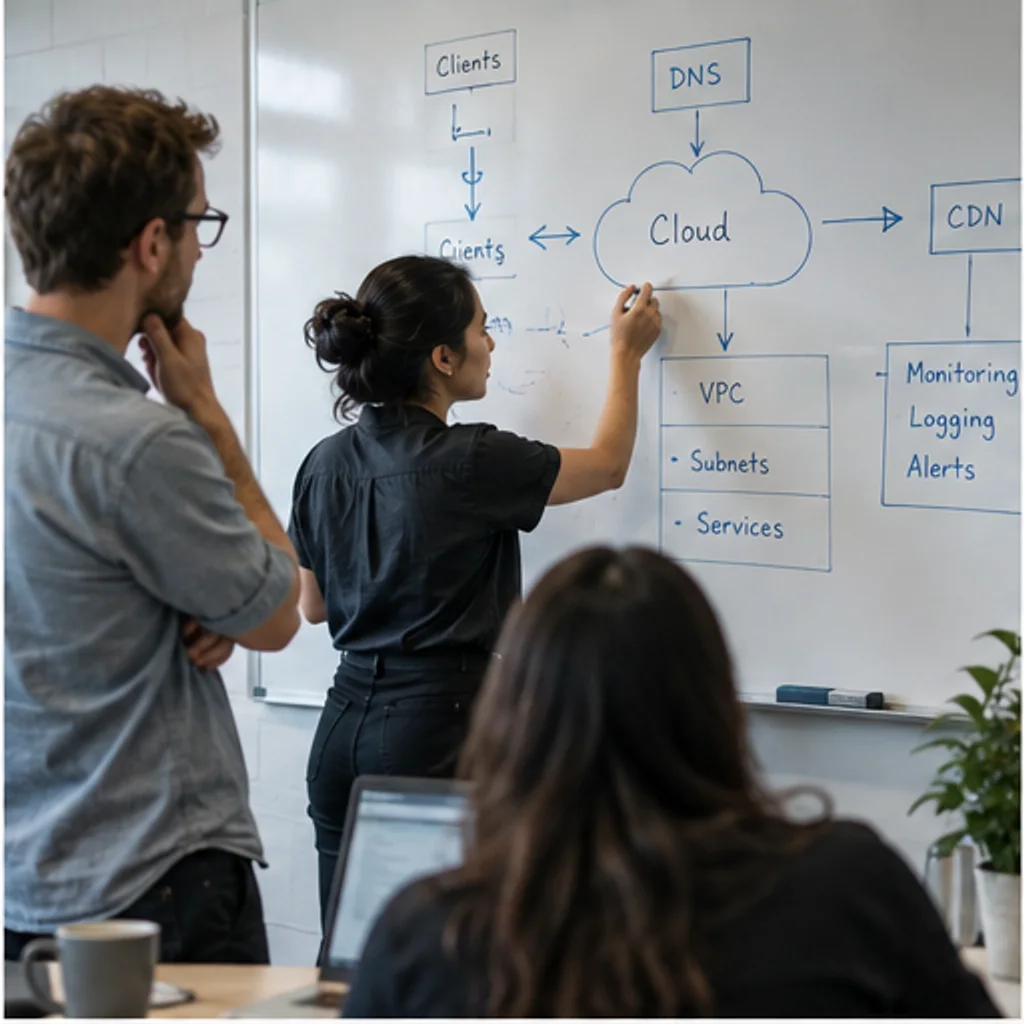
Reduce common exposure
Address common sources of exposure in forms, APIs, dependencies, and configuration. Changes are validated against the functionality users rely on.
- Secure form and API handling
- Configuration hardening
- Patch and credential practices
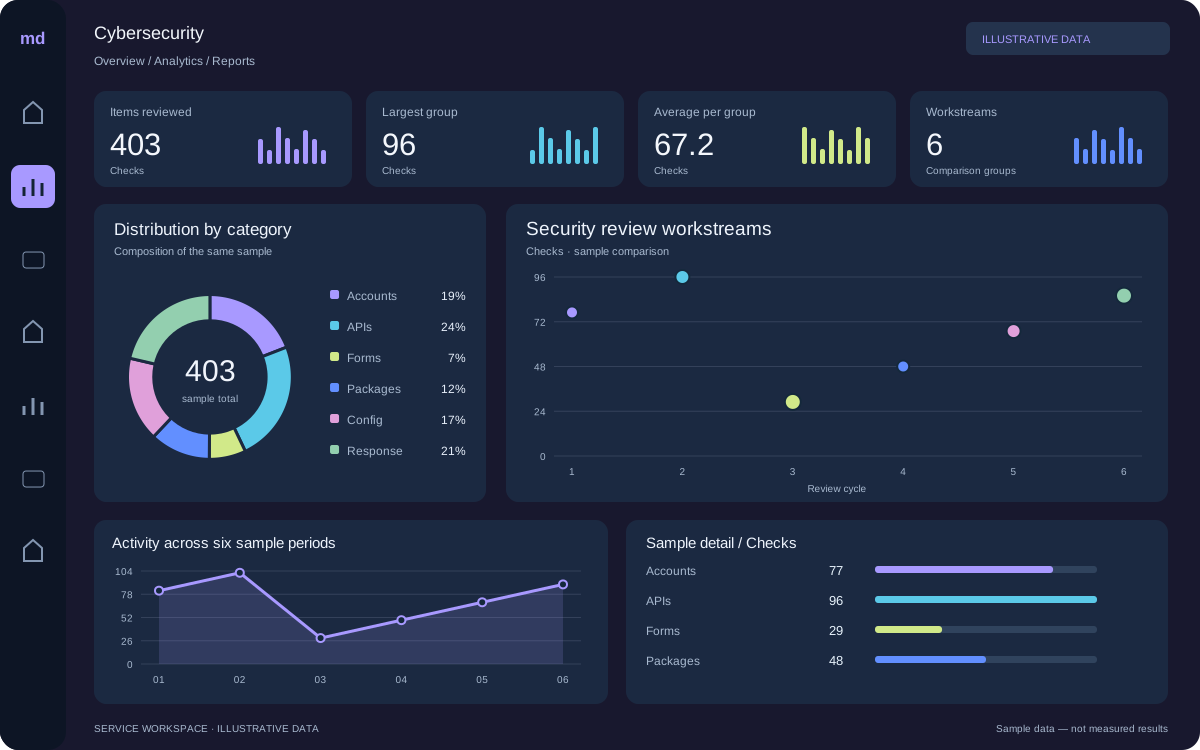
Prepare for security incidents
Prepare the team to recognize and respond to an incident. Clear escalation paths and remediation tracking help turn a finding into a coordinated response.
- Alert routing
- Incident response playbooks
- Remediation tracking
Work with the systems
you depend on.
We review interfaces, permissions, data ownership, and platform limitations before connecting tools. Each handoff includes validation, error handling, and a clear owner.
Make room for
higher-value work.
Use assisted log analysis and incident summaries to help operators investigate faster. Keep production changes behind explicit permissions, reviewed runbooks, and rollback checks.
Explore an opportunity ↗Choose a bounded task
Define the input, expected output, and decisions that stay with people.
Validate with real scenarios
Test representative cases and plan how exceptions reach your team.
Improve from evidence
Review quality, operating cost, and usefulness before expanding.
From first conversation to a working result.
Clear milestones and review points keep the work connected to your goals.
Discover
Review the current workflow, goals, constraints, and available evidence.
Define
Agree the scope, acceptance criteria, responsibilities, and delivery plan.
Deliver & validate
Work in reviewable stages, check the result, and resolve issues before handoff.
Launch & improve
Prepare documentation, confirm ownership, and plan improvements from real use.
Cybersecurity FAQs.
Let’s make the scope and next steps clear.
Ask about your project ↗What is included in Cybersecurity?
Security reviews, access controls, SSL, form protection, dependency checks, hardening, and secure deployment practices. We agree the deliverables, exclusions, and acceptance criteria during discovery so the engagement has a clear scope.
What should we bring to the first conversation?
Share your goals, current tools, and an example of the workflow you want to improve. For this service, useful starting points include application and dependency review, account and access assessment, and sensitive data flow mapping.
Can you work with our existing team and systems?
Yes. We review the current environment, access requirements, and internal responsibilities before recommending changes. The delivery plan can include collaboration with your team, documentation, and knowledge transfer.
How are timelines and ongoing support agreed?
We estimate the work after reviewing scope, dependencies, and access. Milestones, review checkpoints, support hours, and response targets are agreed for the engagement; they are not assumed from the service name.
Cloud Engineering in focus.
A closer look at the collaboration and practical work behind the digital experience.
Illustrative service photography.
What would you like to improve?
Bring us the challenge. We’ll help you shape a practical scope.
Talk to Media Decoding ↗